 Cybersecurity
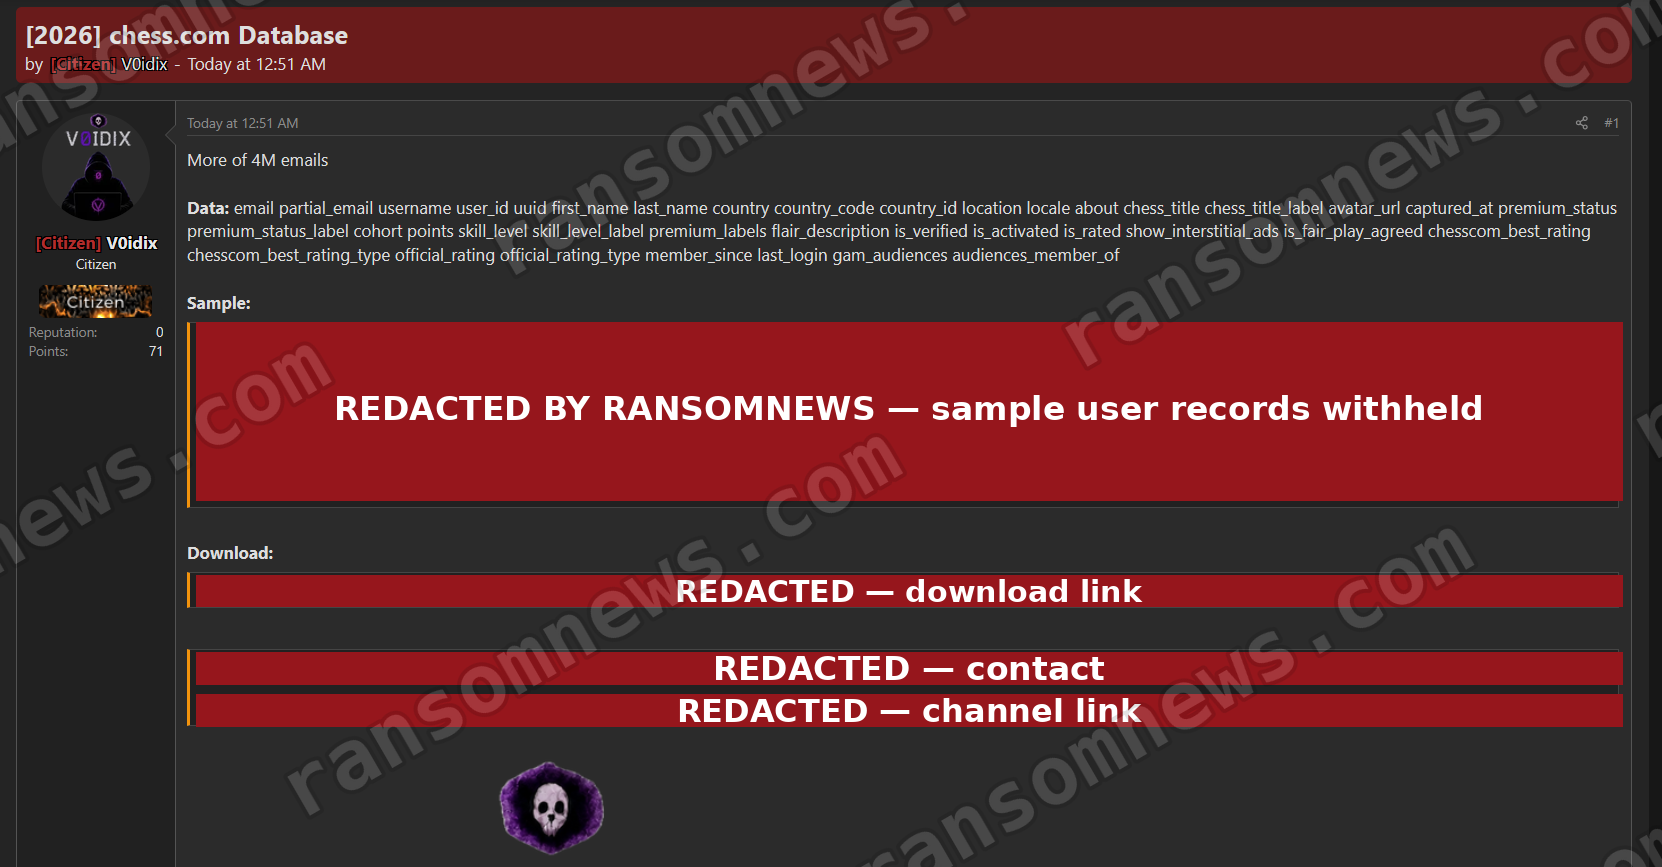
Chess.com Leak Exposes 7.3M Users, Evidence Points to Scraping
A security breach on Chess.com has exposed the personal data of 7.3 million users, with evidence pointing to web scraping as the likely cause. The leak, which was first reported by Security Affairs, is believed to have occurred after a hacker exploited a vulnerability in the website's API. The leaked data includes user IDs, email addresses, and chess ratings. The breach is thought to have occurred in March 2022, with the data being stolen in real-time. The hacker, who has been identified as 'oumou,' has been linked to previous data breaches. The Chess.com website has acknowledged the breach and is urging users to change their passwords. The company has also stated that it is working with law enforcement to investigate the incident. The leak is the latest in a string of high-profile data breaches affecting online gaming and social media platforms. In 2021, a similar breach exposed the data of millions of users on the gaming platform Roblox. The Chess.com breach highlights the need for increased security measures to protect user data in the online gaming and social media space.
Read the full article at securityaffairs.com →